Reverse engineering is a skill best kept fresh, and there’s few better places to practice currently than crackmes.
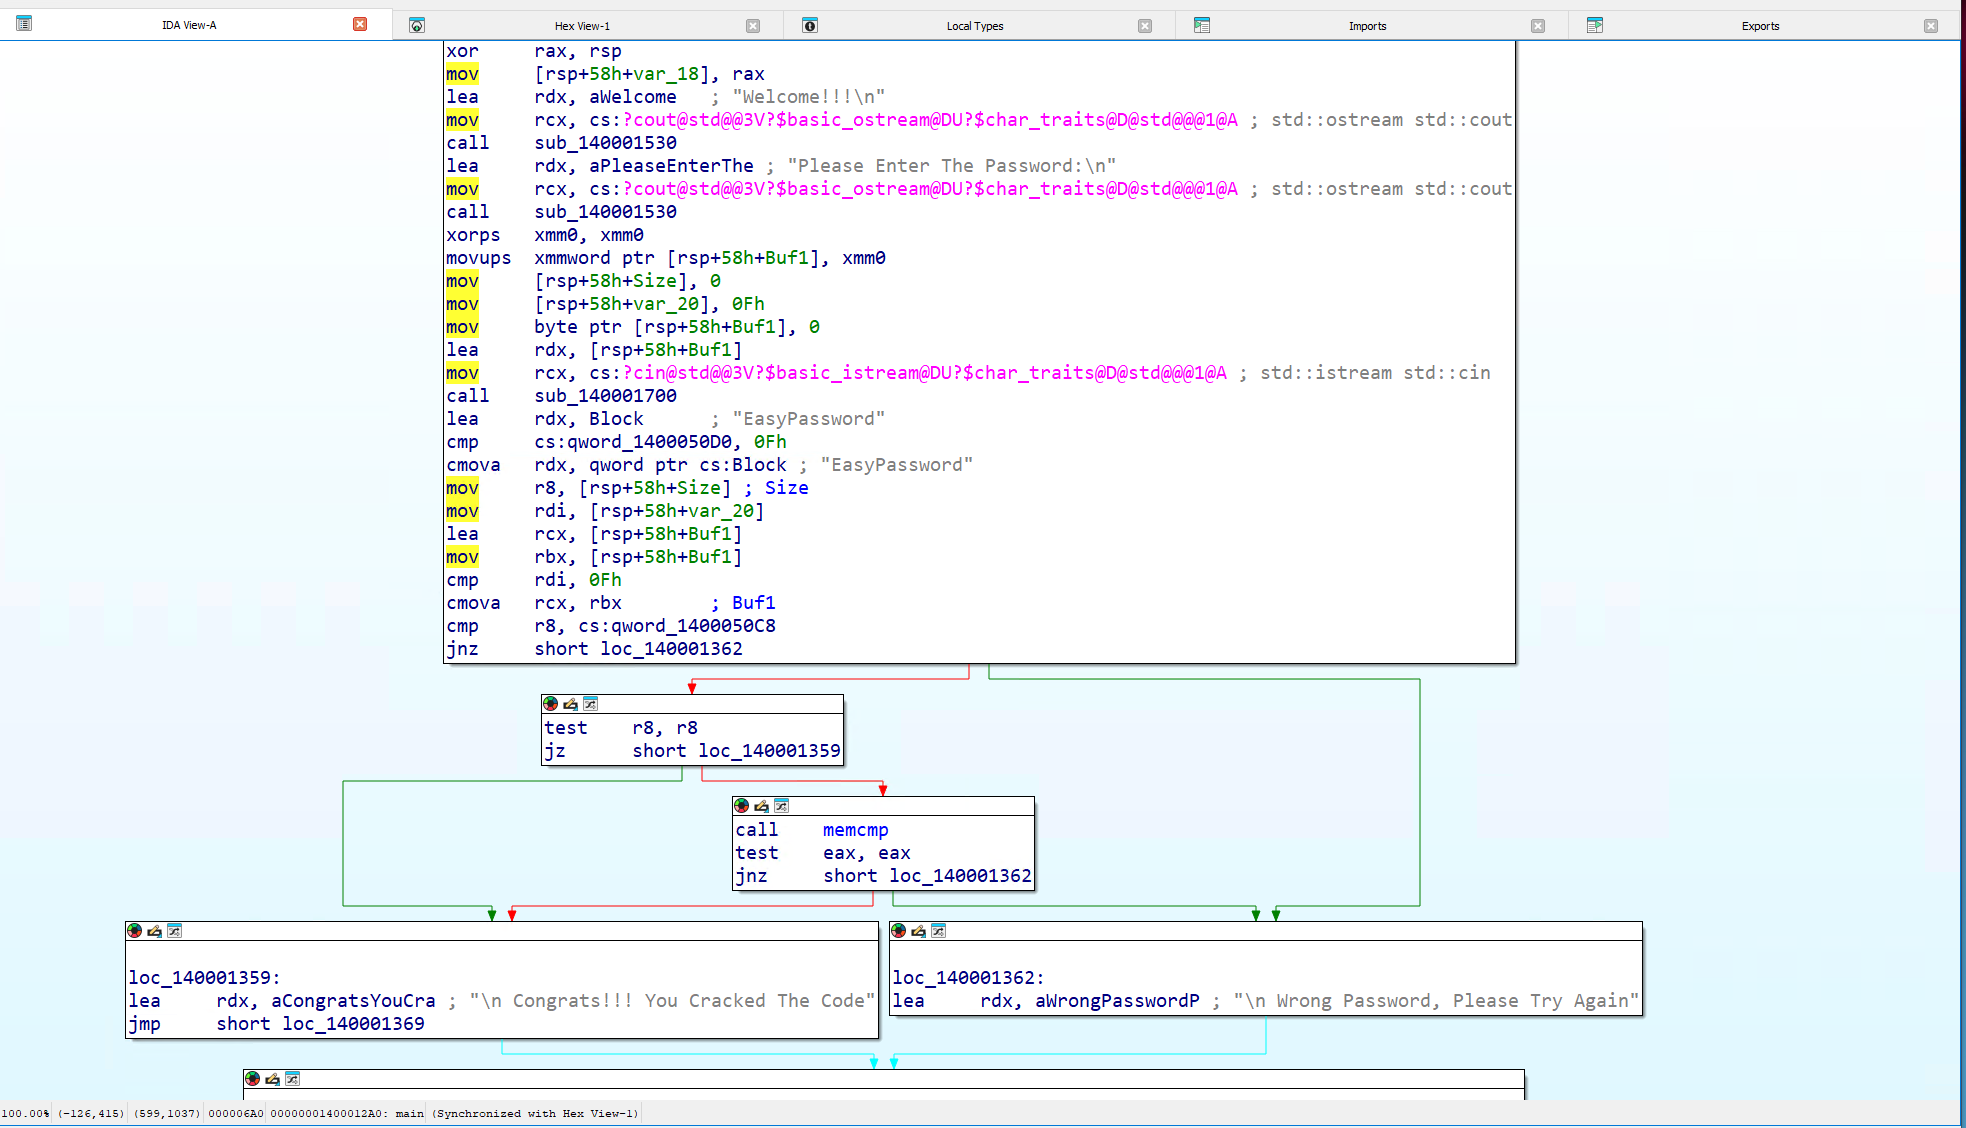
For today, I wanted to get a quick practice in so I decided to tackle an easy level 1 problem with Kanax01’s Fixed Easy Crackme. After moving it into our FLARE-VM, we’re ready to go and crack it open in Ida. Immediately, in the decompiled main function we can see the program takes an input for a password, loads the string “EasyPassword” into memory, then does a memcmp to compare the two values in memory. This is a great start to a hypothesis that the password here is “EasyPassword”.
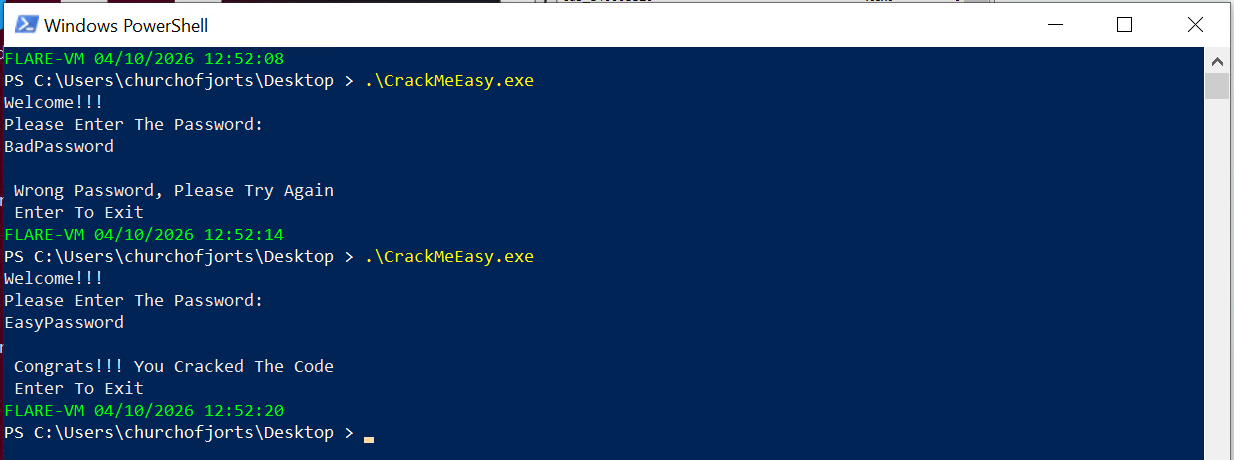
To test the hypothesis, we can run the program with a couple attempts. Yep, just like the crackme description. Can’t get simpler than this.